 Computer Forum
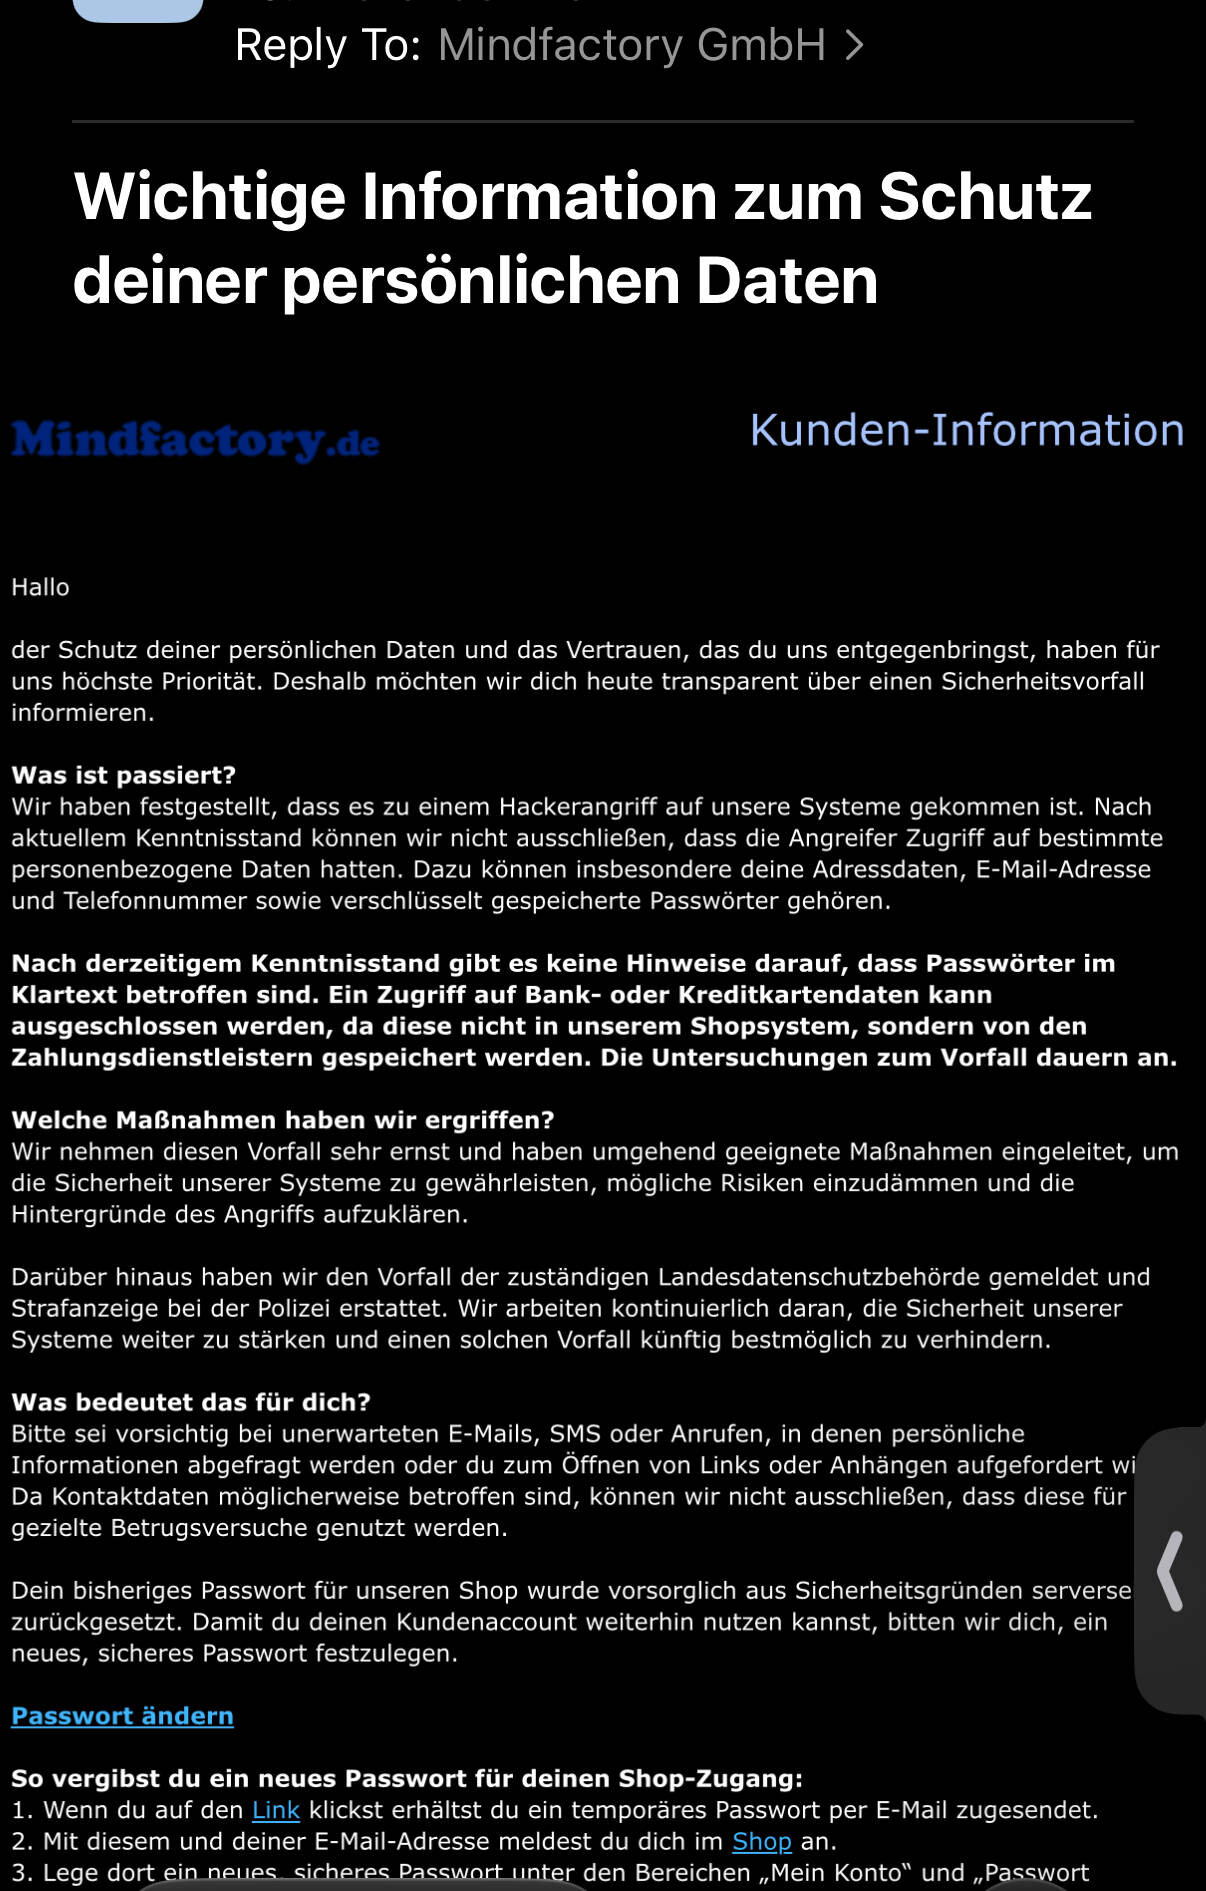 Datenpanne bei Mindfactory (Image © PCMasters.de)
Scope of the Compromised Data
According to the company’s internal investigation, several categories of personal data may have been exposed. The data breach likely includes:
- residential addresses
- email addresses
- customers’ phone numbers.
In addition, the attackers may have gained access to passwords that were stored in encrypted form.
Sensitive financial data is not believed to have been affected by the data breach. Bank account details and credit card information were not accessed, as this data is not stored in the retailer’s own shopping cart system. Instead, this information is managed exclusively by external payment service providers. The company also stated that passwords in plain text were not compromised.
Security Measures and Account Recovery
In response to the incident, Mindfactory has implemented a mandatory password reset for all user accounts as a precautionary measure. To regain access to their accounts, affected users must follow a specific recovery process:
-
- Users will receive a link via email through which they can obtain a temporary password.
-
- Once they have logged in to the store using the temporary login credentials, users must navigate to the “My Account” and “Change Password” sections.
-
- A new, secure password must be set before the account can be used for further transactions.
Legal Action and Compliance with Regulatory Requirements
Following the data breach, Mindfactory took formal steps to comply with legal and regulatory requirements. The company officially notified the relevant state data protection authority to ensure compliance with data protection laws. In addition, a criminal complaint was filed with the police to initiate a formal investigation into the source and nature of the attack.
Warning About Phishing and Social Engineering
The retailer has explicitly warned its customers about the risk of follow-up attacks. Since contact information such as phone numbers and email addresses may have been stolen, there is a high likelihood that this data will be used for targeted phishing campaigns. Customers are advised to exercise extreme caution when receiving unexpected emails, text messages, or phone calls. In particular, users should be suspicious if messages ask for personal information or login credentials, or if the recipient is urged to click on external links or download attachments.
This incident follows a similar security breach at another online retailer, Notebooksbilliger. Although both incidents occurred within a short period of time, it is not yet clear whether there is a direct connection between the two attacks. Mindfactory has not yet disclosed the total number of people affected, the exact date of the incident, or the specific technical vulnerability that the attackers exploited to gain access to the system.